Privacy exposure
Central biometric stores concentrate sensitive data, regulatory risk and breach impact.
Privacy-first trust infrastructure
PalmVault binds a credential to its rightful holder and verifies access or payment rights at the edge without sending biometrics to a central database.
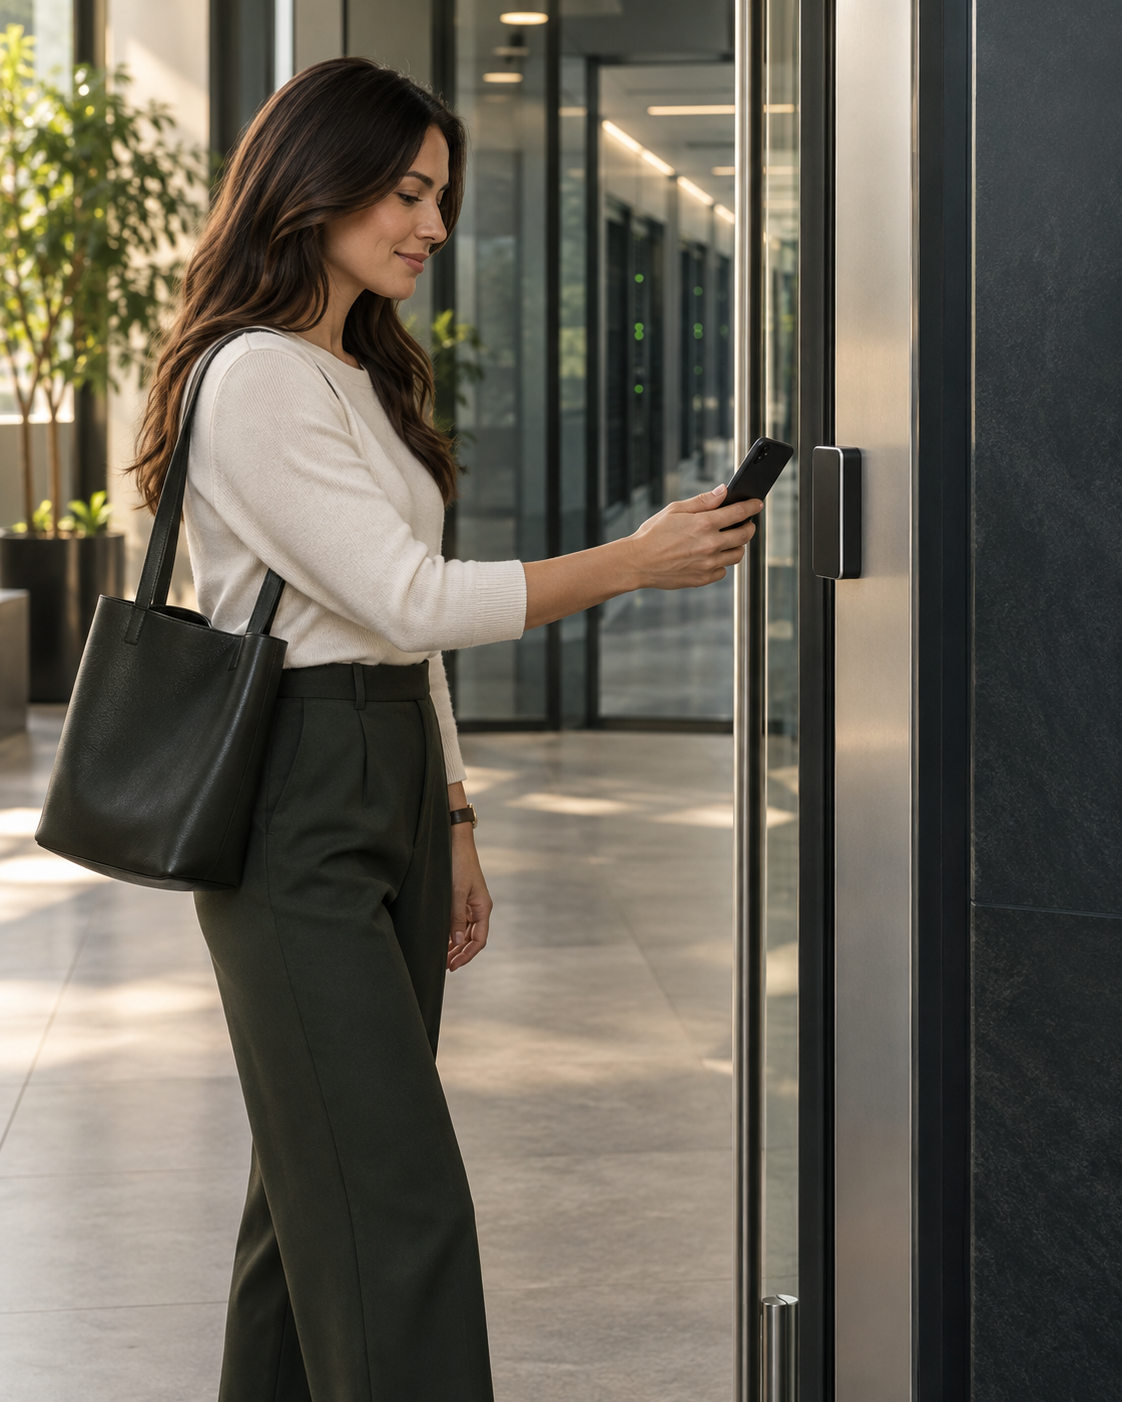
Centralised access creates a single high-value target, and connectivity becomes a point of failure. PalmVault moves the critical trust decision closer to where it is needed.
Central biometric stores concentrate sensitive data, regulatory risk and breach impact.
When networks or cloud services fail, connected credentials can stop working at the moment they matter.
A valid pass does not always prove that the person presenting it is the person entitled to use it.
PalmVault combines on-device authentication, cryptographic proof and portable entitlement tokens in one privacy-first flow.
The edge device issues a fresh cryptographic challenge for the session.
The user proves presence with their device biometric. The biometric never leaves the device.
The signed response and entitlement token are checked locally.
The edge grants or denies access, service or payment according to embedded rules.
The same locally verified entitlement can govern doors, devices, services, quotas and transactions at the edge.
Face or fingerprint verification happens through the user’s own device. PalmVault does not need a central biometric database.
Local validation is designed to keep critical flows moving when the internet, cloud or central service is unavailable.
PalmVault is for operators where identity, permissions and continuity are operational, not cosmetic.
Bind access rights to a live authorised person, with decisions made on site.
Control time-bound, role-based access across changing workforces and restricted zones.
Maintain trusted access when connectivity is degraded, denied or deliberately disrupted.
Extend proven high-assurance infrastructure into frictionless everyday access and payments.
We are speaking with pilot partners, access-control integrators and investors building the next generation of secure physical infrastructure.